


[Nov-2023] 5V0-41.21 Exam Questions and Valid 5V0-41.21 Dumps PDF
5V0-41.21 Brain Dump: A Study Guide with Tips & Tricks for passing Exam
VMware 5V0-41.21 certification exam covers a range of topics related to security in VMware NSX-T Data Center 3.1. These topics include network security, micro-segmentation, distributed firewalls, VPN, and SSL VPN. Candidates will also learn about advanced security features such as IDS/IPS, distributed IDS/IPS, and network introspection. 5V0-41.21 exam tests the candidate's understanding of these topics and their ability to apply this knowledge to real-world scenarios.
NEW QUESTION # 28
Which two are true of the NSX Gateway Firewall? (Choose two.)
- A. Firewall rules in System category cannot be edited.
- B. Firewall rules in Pre Rule category are applied to all gateways.
- C. NAT service can be configured in NSX Gateway Firewall policy.
- D. Applied-To can be configured at Firewall Policy level.
- E. Security Groups can be used in Applied-To column.
Answer: B,D
NEW QUESTION # 29
At which OSI Layer do Next Generation Firewalls capable of analyzing application traffic operate?
- A. Layer 3
- B. Layer 2
- C. Layer 4
- D. Layer 7
Answer: D
NEW QUESTION # 30
Which is an insertion point for East-West service insertion?
- A. Guest VM vNlC
- B. transport node
- C. tier-1 gateway
- D. Partner SVM
Answer: C
NEW QUESTION # 31
What is an unprotected traffic flow in NSX Intelligence?
- A. A traffic flow that matches the default distributed firewall rule.
- B. A traffic flow that matches a reject rule more granular than the default.
- C. A traffic flow that matches an allow rule more granular than the default.
- D. A traffic flow that matches a drop rule more granular than the default.
Answer: A
Explanation:
An unprotected traffic flow in NSX Intelligence is a traffic flow that matches the default distributed firewall rule. The default rule is a catch-all rule which allows all traffic to pass through the distributed firewall, and any traffic flows that match this rule will be marked as unprotected. NSX Intelligence will then generate an alert for any unprotected traffic flows, allowing the administrator to take action to secure the traffic flow. Reference: [1] https://docs.vmware.com/en/VMware-NSX-T/3.0/vmware-nsx-t-30-administration-guide/GUID-D43B9C85-7F4C-4504-8D2B-BC1D7CADB4CD.html [2] https://www.vmware.com/content/dam/digitalmarketing/vmware/en/pdf/techpaper/vmware-nsx-data-center-for-vsphere-distributed-firewall-deployment-guide.pdf
NEW QUESTION # 32
A Security Administrator needs to update their NSX Distributed IDS/IPS policy to detect new attacks with critical CVSS scoring that leads to credential theft from targeted systems.
Which actions should you take?
- A. * Edit your Distributed IDS rule from Security > Distributed IDS/IPS > Rules
* Filter on attack type and select Successful Credential Theft Detected
* Update Mode to detect and prevent
* Click on gear icon and change direction to OUT - B. * Edit your Distributed IDS rule from Security > Distributed IDS/IPS > Rules
* Filter on attack type and select Successful Credential Theft Detected
* Update Mode to detect and prevent
* Click on gear icon and change direction to IN-OUT - C. * Update Distributed IDS/IPS signature database
* Edit your profile from Security > Distributed IDS > Profiles
* Select Critical severity, filter on attack type and select Successful Credential Theft Detected
* Check the profile is applied in Distributed IDS rules - D. * Create a new profile from Security > Distributed IDS > Profiles
* Select Critical severity, filter on attack type and select Successful Credential Theft Detected
* Check the profile is applied In Distributed IDS rules
* Monitor Distributed IDS alerts to validate changes are applied
Answer: C
Explanation:
https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.1/nsxt_31_ids_ips/GUID-B2D6A7F6-
NEW QUESTION # 33
A customer has a requirement to achieve Zero-Trust Security and minimize operational overhead. Which VMware solution can be used by the customer to achieve the requirement?
- A. NSX Intelligence
- B. Carbon Black Anti-Virus
- C. NSX Manager
- D. Tanzu Kubernetes Grid
Answer: A
Explanation:
NSX Intelligence is a security analytics solution from VMware that can be used to achieve Zero-Trust Security and minimize operational overhead. It provides an AI-driven security analytics platform that can detect and respond to threats in real-time, allowing organizations to quickly identify threats and respond to them before they can cause damage. Additionally, it also provides automated security operations and orchestration capabilities that can help reduce manual overhead and free up resources for more important tasks.
For more information on NSX Intelligence and how it can help achieve Zero-Trust Security and minimize operational overhead, please refer to the NSX-T Data Center documentation: https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.0/nsx-t-3.0-intelligence/GUID-C2B2AF2E-A76A-46B8-A67A-42D7A9E924A9.html
NEW QUESTION # 34
Which three criteria help to determine the severity for a Distributed IDS/IPS? (Choose three.)
- A. The severity specified in the signature itself
- B. The Distributed Intrusion Detection and Intrusion Prevention rules.
- C. The load balancer deployment type.
- D. The type-rating associated with the classification type.
- E. The Common Vulnerability Scoring System score specified in the signature.
Answer: A,D,E
Explanation:
For further reading, see the VMware NSX-T Data Center Administration Guide (https://pubs.vmware.com/NSX-T-Data-Center/index.html#com.vmware.nsxt.admin.doc/GUID-E6B25C6F-1F25-4B0F-B8AF-6B8C00F9C3A3.html) for more information on configuring the Distributed IDS/IPS.
NEW QUESTION # 35
To which object can time based rules be applied?
- A. DFW only
- B. DFW or Gateway Firewall, but not both at the same time
- C. DFW and Gateway Firewall both
- D. Gateway Firewall only
Answer: C
NEW QUESTION # 36
Which three criteria help to determine the severity for a Distributed IDS/IPS? (Choose three.)
- A. The severity specified in the signature itself
- B. The type-rating associated with the classification type.
- C. The Common Vulnerability Scoring System score specified in the signature.
- D. The load balancer deployment type.
- E. The Distributed Intrusion Detection and Intrusion Prevention rules.
Answer: A,D,E
NEW QUESTION # 37
An administrator wants to use Distributed Intrusion Detection. How is this implemented in an NSX-T Data Center?
- A. As a distributed solution across multiple KVM hosts.
- B. As a distributed solution across multiple NSX Edge nodes.
- C. As a distributed solution across multiple NSX Managers.
- D. As a distributed solution across multiple ESXi hosts.
Answer: B
Explanation:
An administrator can implement Distributed Intrusion Detection as a distributed solution across multiple NSX Edge nodes in an NSX-T Data Center. This allows for real-time monitoring of network traffic, as well as detection and prevention of malicious activity. Additionally, it can be used to identify, investigate, and respond to potential security threats. Reference: [1] https://docs.vmware.com/en/VMware-NSX-T/3.0/vmware-nsx-t-30-administration-guide/GUID-1F8741C0-D1CD-4EA3-A2BB-98CEF7F8D1DA.html [2] https://www.vmware.com/content/dam/digitalmarketing/vmware/en/pdf/techpaper/vmware-nsx-data-center-for-vsphere-distributed-intrusion-detection-deployment-guide.pdf
NEW QUESTION # 38
What is the default action of the Default Layer 3 distributed firewall rule?
- A. Drop
- B. Reject
- C. Allow
- D. Forward
Answer: D
NEW QUESTION # 39
Which esxcli command lists the firewall configuration on ESXi hosts?
- A. esxcli network firewall ruleset list
- B. vsipioct1 getrules -f <filter-name>
- C. esxcli network firewall rules
- D. vsipioct1getrules -filter <filter-name>
Answer: A
NEW QUESTION # 40
How does N5X Distributed IDS/IPS keep up to date with signatures?
- A. NSX Distributed IDS/IPS signatures are retrieved from updates.vmware.com.
- B. NSX Manager has a local IDS/IPS signatures database that does not need to be updated.
- C. NSX Edge uses manually uploaded signatures by the security administrator.
- D. NSX-T Data Center is using a cloud based database to download the IDS/IPS signatures.
Answer: A
NEW QUESTION # 41
Which two Guest OS drivers are required for the Identity Firewall to operate? (Choose two.)
- A. vmxnet3
- B. e1000e
- C. NSX Network Introspection
- D. NSX File Introspection
- E. Guest Introspection
Answer: C,E
Explanation:
The two Guest OS drivers that are required for the Identity Firewall to operate are NSX Network Introspection and Guest Introspection. NSX Network Introspection provides network-level visibility and control, while Guest Introspection provides kernel-level visibility and control. The other drivers listed, vmxnet3, NSX File Introspection, and e1000e, are not required for the Identity Firewall to operate.
NEW QUESTION # 42
When using URL Analysis In NSX-T, which two services must be set in the URL rule to capture traffic over TCP and UDP? (Choose two.)
- A. DNS
- B. DHCP
- C. DNS-UDP
- D. DHCPv6
- E. DNS-TSIG
Answer: A,B
NEW QUESTION # 43
What needs to be configured on each transport node prior to using NSX-T Data Center Distributed Firewall time-based rule publishing?
- A. PAT
- B. DNS
- C. NAT
- D. NTP
Answer: D
Explanation:
In order to use NSX-T Data Center Distributed Firewall time-based rule publishing, the NTP (Network Time Protocol) needs to be configured on each transport node. This ensures that the transport nodes have accurate time synchronization, which is required for time-based rule publishing. Additionally, DNS (Domain Name System) and PAT (Port Address Translation) may also need to be configured on each transport node, depending on the desired configuration. Reference: [1] https://docs.vmware.com/en/VMware-NSX-T/2.5/com.vmware.nsxt.admin.doc/GUID-E9F8D8AD-7AF1-4F09-B62C-6A17A6F39A6C.html [2] https://docs.vmware.com/en/VMware-NSX-T/2.4/com.vmware.nsxt.admin.doc/GUID-E9F8D8AD-7AF1-4F09-B62C-6A17A6F39A6C.html
NEW QUESTION # 44
Which two are true of the NSX Gateway Firewall? (Choose two.)
- A. Firewall rules in System category cannot be edited.
- B. Firewall rules in Pre Rule category are applied to all gateways.
- C. Applied-To can be configured at Firewall Policy level.
- D. NAT service can be configured in NSX Gateway Firewall policy.
- E. Security Groups can be used in Applied-To column.
Answer: B,E
Explanation:
NSX Gateway Firewall is a distributed firewall that provides security for east-west traffic within a virtual environment.
1. Firewall rules in Pre Rule category are applied to all gateways. This category contains system-defined rules that are always applied first to all gateways and cannot be modified. These rules include the default deny all rule and others that control basic connectivity.
2. Security Groups can be used in Applied-To column. Security groups allow you to group together VMs that have similar security requirements and then apply firewall policies to those groups. This way you can apply the same security rules to multiple VMs at once, instead of configuring the rules on each individual VM.
Reference:
VMware NSX-T Data Center documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/index.html VMware NSX-T Data Center Gateway Firewall documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.1/com.vmware.nsxt.firewall.doc/GUID-4C5D5A5F-8FDF-4F2A-9C5A-2C1903A3E5A5.html
NEW QUESTION # 45
Which dot color indicates an on-going attack of medium severity in the IDS/IPS events tab of NSX-T Data Center?
- A. blinking yellow dot
- B. solid red dot
- C. blinking orange dot
- D. solid orange dot
Answer: D
Explanation:
The dot color that indicates an on-going attack of medium severity in the IDS/IPS events tab of NSX-T Data Center is a solid orange dot. This indicates that the attack has been detected and is ongoing at a medium severity level.
Reference:
In the IDS/IPS events tab of NSX-T Data Center, different colors of dots are used to indicate the severity of an attack.
A solid red dot indicates a critical attack, which is the highest severity level.
A solid orange dot indicates a medium attack, which is a moderate severity level.
A solid yellow dot indicates a low attack, which is the lowest severity level.
In this case, a solid orange dot is used to indicate an on-going attack of medium severity in the IDS/IPS events tab of NSX-T Data Center.
It's worth noting that there is no blinking dots in this context, all the dots are solid.
VMware NSX-T Data Center documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/index.html VMware NSX-T Data Center Intrusion Detection and Prevention documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.1/com.vmware.nsxt.ids.doc/GUID-C4ED1F4D-4E4B-4A9C-9F5C-7AC081A5C5D5.html
NEW QUESTION # 46
Which are the four use cases for NSX Tags?
- A. Manageability, Third-party sharing/context sharing, Security, and Troubleshooting (Traceability)
- B. Manageability, Third-party sharing/context sharing. Security, and Logging
- C. Accountability, Third-party sharing/context sharing, Security, and Troubleshooting (Traceability)
- D. Accountability, Third-party sharing/context sharing. Security, and Logging
Answer: C
NEW QUESTION # 47
Refer to the exhibit.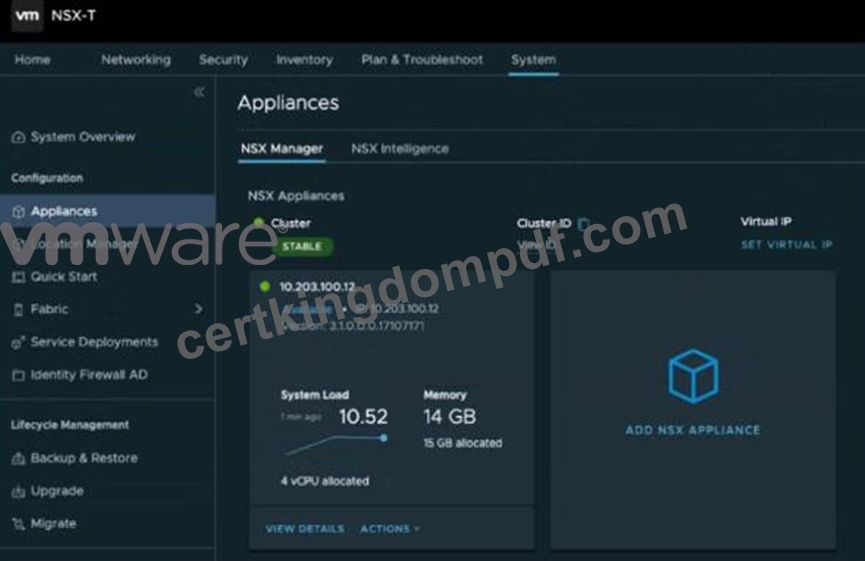
Referencing the exhibit, what is the VMware recommended number of NSX Manager Nodes to additionally deploy to form an NSX-T Manager Cluster?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: A
NEW QUESTION # 48
Refer to the exhibit.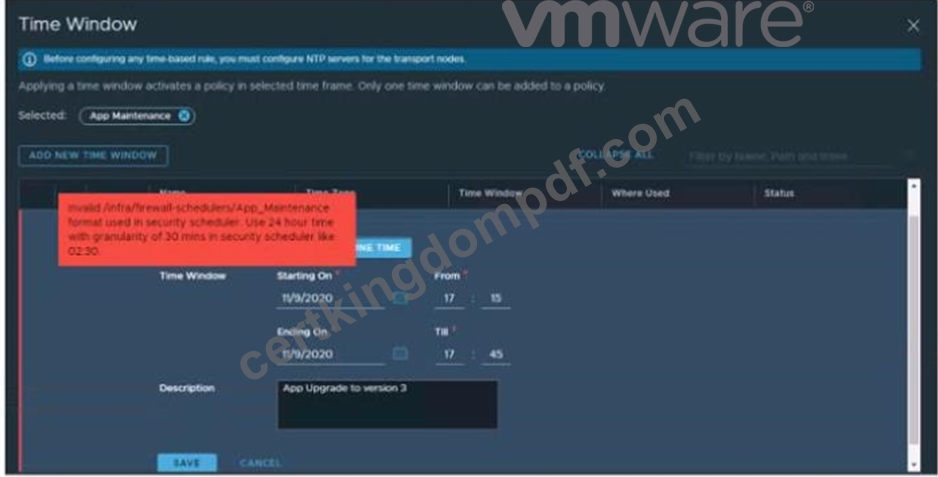
A security administrator is configuring a time window to create a time-based distributed firewall rule. While configuring the time window, an error displayed as shown in the exhibit. Which action will resolve the problem?
- A. Change the time window interval.
- B. Change the time windows frequency
- C. Configure the ESXl host to use a remote NTP server.
- D. Restart me NTP service on the ESXl host.
Answer: C
Explanation:
The most likely action to resolve the problem is to configure the ESXi host to use a remote NTP server. The time window requires the ESXi host to be synchronized to a time source in order to properly calculate the time window, and the error is likely due to the ESXi host not being synchronized. Configuring the ESXi host to use a remote NTP server should ensure that the host is properly synchronized, and allow the time window to be configured correctly. Reference: [1] https://docs.vmware.com/en/VMware-NSX-T/3.0/vmware-nsx-t-30-administration-guide/GUID-DD7F38A3-3D3B-47F1-92D7-9A4D4F3C44E1.html [2] https://www.vmware.com/support/vsphere/doc/vsphere-esxi-vcenter-server-601-configuration-maximums.html
NEW QUESTION # 49
An administrator has enabled the "logging" option on a specific firewall rule. The administrator does not see messages on the Logging Server related to this firewall rule. What could be causing the issue?
- A. The logging server on the transport nodes is not configured.
- B. NSX Manager must have Firewall Logging enabled.
- C. Firewall Rule Logging is only supported in Gateway Firewalls.
- D. The logging on the firewall policy needs to be enabled.
Answer: C
NEW QUESTION # 50
What must an administrator deploy to provide Linux based VMs with antivirus protection?
- A. Guest Customization Agent
- B. Antivirus Agent in vCenter
- C. Guest Introspection Thin Agent
- D. Antivirus Agent in NSX
Answer: C
Explanation:
NSX provides a feature called Guest Introspection that allows administrators to provide security services to virtual machines, including antivirus protection. One of the components of Guest Introspection is the Guest Introspection Thin Agent, which must be deployed to provide Linux-based VMs with antivirus protection. The Thin Agent is a lightweight agent that runs inside the guest operating system of virtual machines and communicates with the NSX Manager to provide security services.
Once the Guest Introspection Thin Agent is deployed, the administrator can configure the antivirus service to scan virtual machines for malware and take action on any threats that are detected.
Reference:
VMware NSX Guest Introspection documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.1/com.vmware.nsxt.guest_introspection.doc/GUID-A86FBAF1-A8D9-4E12-8F3D-04B3D89B8F7E.html VMware NSX Guest Introspection Thin Agent documentation https://docs.vmware.com/en/VMware-NSX-T-Data-Center/3.1/com.vmware.nsxt.guest_introspection.doc/GUID-A86FBAF1-A8D9-4E12-8F3D-04B3D89B8F7E.html
NEW QUESTION # 51
An administrator needs to configure their NSX-T logging to audit changes on firewall security policy. The administrator Is using the following command from NSX-T3.1 documentation :
Which Message ID from the following list will allow the administrator to track changes on firewall security rules?
- A. MONITOR
- B. FIREWALL
- C. FABRIC
- D. SYSTEM
Answer: B
Explanation:
The message ID that will allow the administrator to track changes on firewall security rules is "FIREWALL". This message ID is part of the NSX-T3.1 documentation and will be used to log any changes made to the firewall security policy. This will allow the administrator to easily audit and track any changes made to the policy. Reference: [1] https://docs.vmware.com/en/VMware-NSX-T/3.1/nsx_31_logging_guide/GUID-ADEDE32F-0606-4C2F-81B2-71914EEDA11F.html [2] https://www.vmware.com/content/dam/digitalmarketing/vmware/en/pdf/products/nsx/vmware-nsx-data-center-logging-guide.pdf
NEW QUESTION # 52
......
5V0-41.21 Exam Questions: Free PDF Download Recently Updated Questions: https://www.certkingdompdf.com/5V0-41.21-latest-certkingdom-dumps.html