


Hesitation is natural before any purchase, which is why CertkingdomPDF publishes a free demo for the CS0-001 exam materials. Download the sample, look through part of the 458 practice questions for the CompTIA Cybersecurity Analyst (CySA+) Certification exam, and let your own judgment replace guesswork before you spend anything.
CompTIA CS0-001 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Cybersecurity Analyst (CySA+) Certification Exam |
| Exam Number: | CS0-001 |
| Exam Duration: | 165 minutes |
| Passing Score: | 750 (on a scale of 100-900) |
| Related Certifications: | CompTIA Security+ CompTIA PenTest+ CompTIA CASP+ |
| Certificate Validity Period: | 3 years |
| Real Exam Qty: | 85 (maximum) |
| Exam Price: | USD 349 |
| Available Languages: | English, Japanese |
| Exam Format: | Multiple Choice, Performance-Based Questions |
| Sample Questions: |  |
| Exam Way: | Pearson VUE testing centers or online proctored exam |
| Pre Condition: | No formal prerequisite. CompTIA recommends Network+, Security+ or equivalent knowledge and 3-4 years of hands-on information security experience. |
| Official Syllabus URL: | https://www.comptia.org/certifications/cybersecurity-analyst |
CompTIA CS0-001 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Security Architecture and Tool Sets | 16% | - Security Tools
|
| Threat Management | 27% | - Threat Detection
|
| Vulnerability Management | 26% | - Vulnerability Remediation
|
| Cyber Incident Response | 31% | - Forensics and Investigation
|
Frequently Asked Questions About the CS0-001 Exam
The CS0-001 exam is the official test for the CompTIA Cybersecurity Analyst (CySA+) Certification certification from CompTIA. It measures whether you can apply the skills described in the exam objectives to realistic scenarios. Earning the credential shows employers that your knowledge has been checked against a recognized industry standard, which is why many candidates treat it as essential armor in a competitive job market.
The passing score for the CS0-001 exam is 750 (on a scale of 100-900), and the exam fee is USD 349. Because retakes mean paying the fee again, most candidates prefer to prepare thoroughly first — working through practice questions with expert-verified answers until the exam format feels familiar is a common approach.
CertkingdomPDF focuses on doing a few things well: practice questions aligned with the real CS0-001 exam format, answers verified by experienced experts, free updates for 365 days after purchase, and a support team available around the clock. You can check all of this yourself before buying, because every product page offers a free demo that you can download and even print. There is no pressure and no obligation — the demo exists so you can make up your own mind.
According to the official outline, the main domains of the CS0-001 exam include:
- Threat Management (27%)
- Vulnerability Management (26%)
- Cyber Incident Response (31%)
The 458 practice questions for the CompTIA Cybersecurity Analyst (CySA+) Certification exam at CertkingdomPDF are organized around these objective areas, so your review time maps directly onto what the exam actually tests.
The CS0-001 exam contains 85 (maximum) questions and allows 165 minutes minutes to complete them. That works out to limited time per question, so practicing under similar time pressure beforehand helps you pace yourself on the real day.
No formal prerequisite. CompTIA recommends Network+, Security+ or equivalent knowledge and 3-4 years of hands-on information security experience.
Yes. CertkingdomPDF provides a free demo for the CS0-001 exam product, and all demos on the site are free of charge. The PDF demo can be downloaded to your device and printed out if you prefer reviewing on paper. Trying the demo first is the easiest way to confirm that the question style, difficulty, and layout match what you need for the CompTIA Cybersecurity Analyst (CySA+) Certification exam — no payment and no commitment required.
CompTIA Cybersecurity Analyst (CySA+) Certification Sample Questions:
In order to the leverage the power of data correlation with Nessus, a cybersecurity analyst must first be able to create a table for the scan results.
Given the following snippet of code: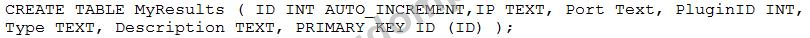
Which of the following output items would be correct?
- A. Option C
- B. Option B
- C. Option A
- D. Option D
Correct Answer: C 🗳️
A security analyst is performing a stealth black-box audit of the local WiFi network and is running a wireless sniffer to capture local WiFi network traffic from a specific wireless access point. The SSID is not appearing in the sniffing logs of the local wireless network traffic. Which of the following is the best action that should be performed NEXT to determine the SSID?
- A. Spoof the MAC addresses of adjacent access points
- B. Set up a fake wireless access point
- C. Deauthorize users of that access point
- D. Power down the wireless access point
Correct Answer: B 🗳️
A vulnerability analyst needs to identify all systems with unauthorized web servers on the 10.1.1.0/24 network. The analyst uses the following default Nmap scan:
nmap -sV -p 1-65535 10.1.1.0/24
Which of the following would be the result of running the above command?
- A. This scan checks all TCP ports and returns versions.
- B. This scan identifies unauthorized servers.
- C. This scan probes all ports and returns open ones.
- D. This scan checks all TCP ports.
Correct Answer: A 🗳️
A company decides to move three of its business applications to different outsourced cloud providers. After moving the applications, the users report the applications time out too quickly and too much time is spent logging back into the different web-based applications throughout the day. Which of the following should a security architect recommend to improve the end-user experience without lowering the security posture?
- A. Create a group policy to extend the default system lockout period.
- B. Configure a web browser to cache the user credentials.
- C. Configure directory services with a federation provider to manage accounts.
- D. Configure user accounts for self-service account management.
Correct Answer: A 🗳️
The director of software development is concerned with recent web application security incidents, including the successful breach of a back-end database server. The director would like to work with the security team to implement a standardized way to design, build, and test web applications and the services that support them. Which of the following meets the criteria?
- A. Ajax
- B. OWASP
- C. SANS
- D. PHP
Correct Answer: B 🗳️
Viewing page 1 out of 92 pages.
Viewing questions 1-5 out of 458 questions.


 Clare

 Murphy

 Melissa

 Myron
 Ellen
 Algernon
 Quintina
 Marico
 Matt
 Sherry
 Regina
 Julius
 Tab
 Jim
 Julie
 Lennon
 Victoria


