


Skeptical? Good — you should be. CertkingdomPDF puts a free CAS-001 demo on the table so you can evaluate the CompTIA Advanced Security Practitioner question quality before paying, not after.
CompTIA CAS-001 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Advanced Security Practitioner |
| Exam Number: | CAS-001 |
| Exam Duration: | 150 minutes |
| Exam Price: | $399 USD (original launch price) |
| Related Certifications: | CompTIA Security+ CompTIA Network+ |
| Real Exam Qty: | 80 maximum |
| Certificate Validity Period: | 3 years from issue |
| Available Languages: | English |
| Exam Format: | Multiple-choice, Performance-based |
| Passing Score: | Pass/Fail only, no scaled score |
| Recommended Training: | CompTIA Official Study Resources |
| Exam Registration: | CompTIA Certification Registration |
| Sample Questions: |  |
| Exam Way: | Onsite at Pearson VUE testing centers |
| Pre Condition: | Recommended: 10 years of IT administration experience including 5 years hands-on technical security experience; CompTIA Security+ or equivalent knowledge |
| Official Syllabus URL: | https://www.comptia.jp/pdf/CASP_objectives.sflb.pdf |
CompTIA CAS-001 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Research & Analysis | 14% | - Strategic security research
|
| Risk Management, Policy/Procedure and Legal | 24% | - Risk assessment and strategy
|
| Integration of Computing, Communications, and Business Disciplines | 22% | - Secure systems integration
|
| Enterprise Security | 40% | - Security controls and architecture
|
Everything About the CompTIA Advanced Security Practitioner — FAQ
Head to the vendor's official registration channels:
One detail worth checking at booking: the CAS-001 exam runs Onsite at Pearson VUE testing centers, so choose the format you are most comfortable with.
The vendor officially recommends:
Take the courses for the theory, then switch to measurement: the CAS-001 practice questions from CertkingdomPDF — with auto-graded mock tests — show you what is actually sticking.
You're looking at 80 maximum questions in 150 minutes. Do the math early, not in the exam room: decide your per-question pace, practice skipping hard items without panic, and finish at least two full timed mock tests — the CertkingdomPDF engine grades them automatically in about a minute, so you get instant feedback on where your time goes.
Delivery is the easy part: pay, click the email link that arrives within a minute, and the CAS-001 files download in about a minute — no extra software, no installation limits. If 2 hours pass with nothing, our support team will fix it. The refund side runs on clear rules: take the corresponding CAS-001 exam within 60 days of purchase, and if you fail, submit a scanned enrollment slip plus the official Score Report PDF within 2 days of the exam for a 100% refund, processed within 7 days. Exams sat within 3 days of purchase don't qualify, candidate and payer names must match, and free or expired products are excluded. Prefer an exchange? Take two equal-value exam products free of charge and keep your original updates.
You need Pass/Fail only, no scaled score to pass, and registration costs $399 USD (original launch price) at the official rate. One uncomfortable truth: the fee is per attempt, so a fail means paying it again. Candidates who self-test first — with auto-graded mock exams built from the 495 questions at CertkingdomPDF — tend to pay that fee exactly once.
The vendor's blueprint for the CompTIA Advanced Security Practitioner has 4 domains, led by Risk Management, Policy/Procedure and Legal (24%), Enterprise Security (40%), Integration of Computing, Communications, and Business Disciplines (22%). The weighting is a study plan in disguise — heavy domains deserve heavy hours. You'll find every domain and subtopic in the complete outline above.
Passing the CAS-001 exam earns the CompTIA Advanced Security Practitioner (CASP) certification — a Expert / Mastery-level credential — issued directly by CompTIA. It is proof of ability that travels well across employers and borders. The credential also links to CompTIA Security+, CompTIA Network+, so it can be a first step rather than a final destination.
Yes — the free PDF demo shows the real question quality before any payment. And the value continues after purchase: 365 days of free updates come standard, with a 50% renewal discount if your update period ever expires.
Recommended: 10 years of IT administration experience including 5 years hands-on technical security experience; CompTIA Security+ or equivalent knowledge These rules do get revised, so before you book, double-check the current requirements on the official CAS-001 exam page — what the vendor publishes is what counts.
CompTIA Advanced Security Practitioner Sample Questions:
The security administrator reports that the physical security of the Ethernet network has been breached, but the fibre channel storage network was not breached. Why might this still concern the storage administrator? (Select TWO).
- A. The storage network uses FCoE.
- B. The storage network uses switch zoning.
- C. The storage network uses LUN masking.
- D. The storage network uses iSCSI.
- E. The storage network uses vSAN.
Correct Answer: A,D 🗳️
A security administrator was recently hired in a start-up company to represent the interest of security and to assist the network team in improving security in the company. The sales team is continuously contacting the security administrator to answer security questions posed by potential customers/clients. Which of the following is the BEST strategy to minimize the frequency of these requests?
- A. Train the sales team about basic security, and make them aware of the security policies and procedures of the company.
- B. The job description of the security administrator is to assist the sales team; thus the process should not be changed.
- C. Request the major stakeholder hire a security liaison to assist the sales team with security-related questions.
- D. Compile a list of the questions, develop an FAQ on the website, and train the sales team about basic security concepts.
Correct Answer: D 🗳️
CORRECT TEXT
The IDS has detected abnormal behavior on this network Click on the network devices to view device information Based on this information, the following tasks need to be completed:
1. Select the server that is a victim of a SQL injection attack.
2. Select the source of the buffer overflow attack.
3. Modify the access control list (ACL) on the router(s) to ONLY block the buffer overflow attack.
Instructions: Simulations can be reset at any time to the initial state: however, all selections will be deleted.
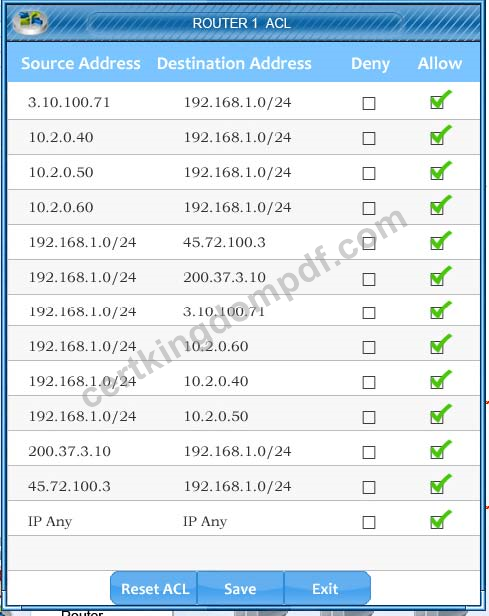

Correct Answer:
Follow the Steps as
Explanation:
First, we need to determine the source of the attack and the victim. View the IDS logs to determine
this information. Although SIMs may vary, one example clearly shows the source of the attack as
the 10.2.0.50 host, and the victim is serverD.
To block only this traffic we need to modify the following rule on router 2 only:
Source address = 10.2.0.50
Destination address = 192.168.1.0/24
Deny box should be checked.
The firm's CISO has been working with the Chief Procurement Officer (CPO) and the Senior Project Manager (SPM) on soliciting bids for a series of HIPS and NIPS products for a major installation in the firm's new Hong Kong office. After reviewing RFQs received from three vendors, the CPO and the SPM have not gained any real data regarding the specifications about any of the solutions and want that data before the procurement continues. Which of the following will the CPO and SPM have the CISO do at this point to get back on track in this procurement process?
- A. Inform the three submitting vendors that there quotes are null and void at this time and that they are disqualified based upon their RFQs.
- B. Ask the three submitting vendors for a full blown RFP so that the CPO and SPM can move to the next step.
- C. Provide the CPO and the SPM a personalized summary from what the CISO knows about these three submitting vendors.
- D. Contact the three submitting vendor firms and have them submit supporting RFIs to provide more detailed information about their product solutions.
Correct Answer: D 🗳️
As part of a new wireless implementation, the Chief Information Officer's (CIO's) main objective is to immediately deploy a system that supports the 802.11r standard, which will help wireless VoIP devices in moving vehicles. However, the 802.11r standard was not ratified by the IETF. The wireless vendor's products do support the pre-ratification version of 802.11r. The security and network administrators have tested the product and do not see any security or compatibility issues; however, they are concerned that the standard is not yet final. Which of the following is the BEST way to proceed?
- A. Do not purchase the equipment now as the client devices do not yet support 802.11r.
- B. Purchase the equipment now, as long as it will be firmware upgradeable to the final 802.11r standard.
- C. Purchase the equipment now, but do not use 802.11r until the standard is ratified.
- D. Do not purchase the equipment now; delay the implementation until the IETF has ratified the final 802.11r standard.
Correct Answer: B 🗳️
Viewing page 1 out of 99 pages.
Viewing questions 1-5 out of 495 questions.


 Ziv

 Lyle

 Gabriel
 Kenneth

 Tracy
 Barbara
 King
 Ingram
 Meredith
 Clementine
 Benson
 Colby
 Sid
 Justin
 Norman
 Brian
 Bing
 Truda


